OptyStack LogoOptyStack Logo
Product
Features
Cost OptimizationCut SaaS waste with discovery, usage-backed rightsizing, and renewal leverage—often up to ~30% savings.Shadow IT DiscoveryDiscover unsanctioned SaaS, shadow AI, and unmanaged subscriptions in one place.License ManagementFind unused seats, eliminate zombie accounts, and automate renewals with usage-backed data.Contract Renewal TrackingOne renewal calendar with notice windows, usage context, and negotiation-ready briefs.Seamless App IntegrationsConnect Microsoft 365, Google Workspace, SSO, and 100+ SaaS brands into one live inventory.Identity Management with Zero Trust SecuritySingle sign-on and conditional access by IP, device, and region for your SaaS apps.
ROI Calculator
Resources

Support

  • Support
  • Knowledge Base
  • SaaS Directory
  • Partners

Content

  • SaaS Inflation Index
  • 2026 SaaS Audit Toolkit
  • Blogs
  • Success Stories
  • Events
PricingAboutContact
Start Free Trial
Book Demo
← All postsBest Practices

What to Do With Your SaaS Audit Results

Aryan Malik · September 24, 2026
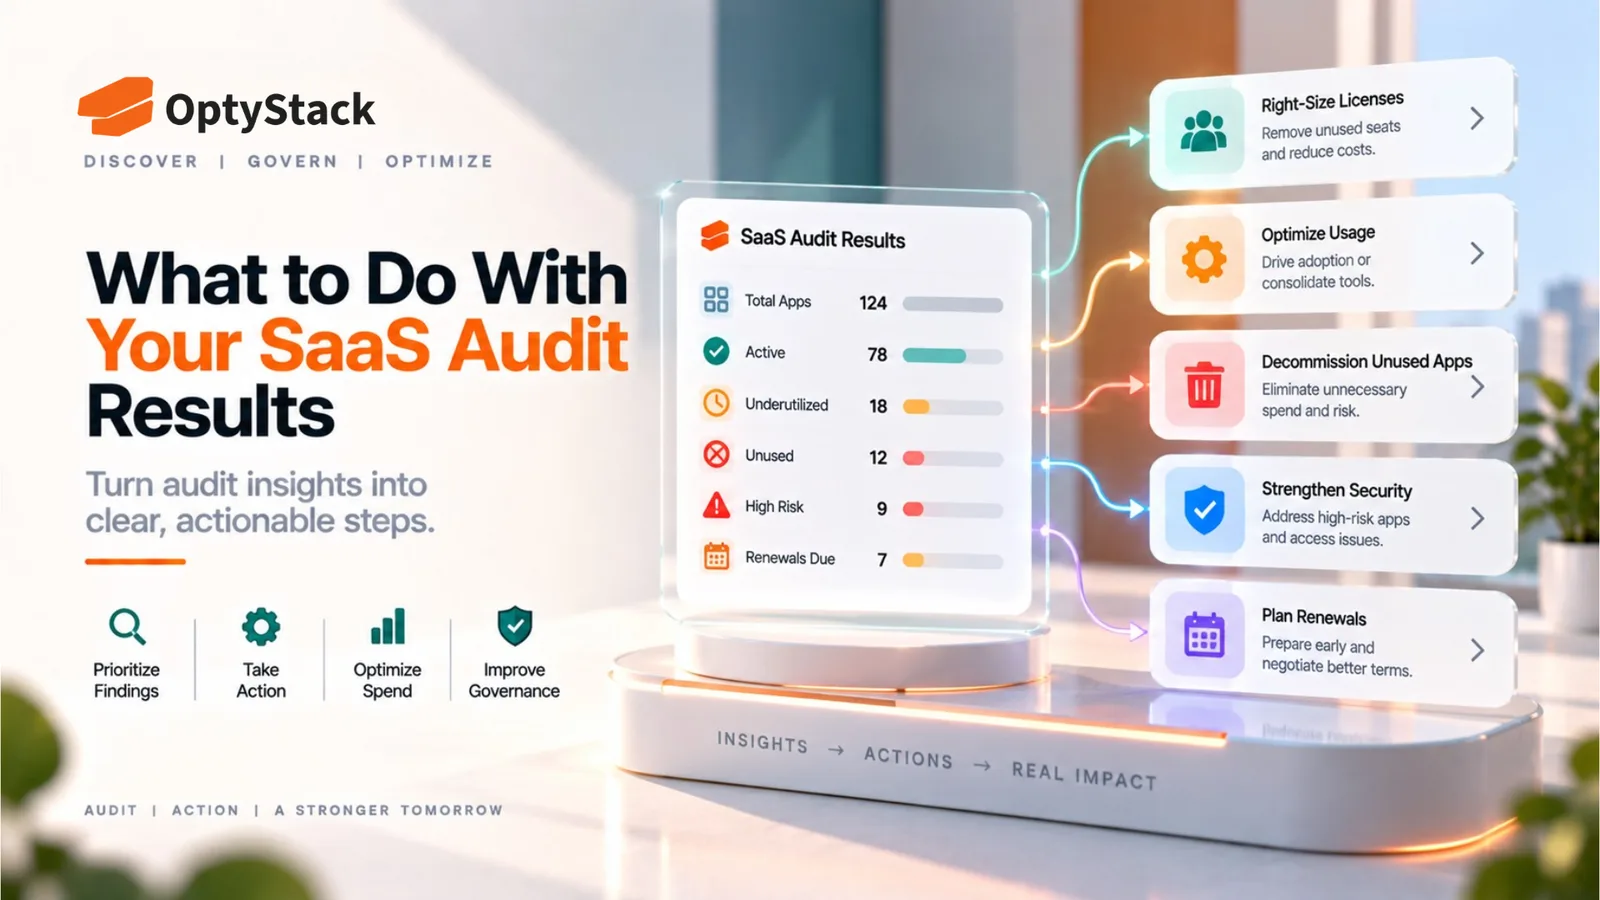
OptyStack SaaS audit results concept showing actionable next steps for right-sizing licenses, optimizing usage, decommissioning unused apps, strengthening security, and planning renewals.
Share
LinkedInX

A finished audit and a useful one aren't the same thing. Here's how to sort your SaaS audit findings, assign real ownership and deadlines, track what actually gets resolved, and fix the process gaps behind recurring waste.

A finished audit and a useful one aren't the same thing. Plenty of SaaS audits produce a thorough, accurate spreadsheet that gets reviewed once, filed away, and referenced again only when the next audit rediscovers the same problems. The value of an audit comes entirely from what happens after it's done, and that's the part most processes treat as an afterthought.

Related reading

Explore related guides and continue your SaaS optimization research:

  • How to Offboard an Employee's AI Agents: A Checklist for IT Teams
  • Microsoft Entra MemberOf Retirement: What IT Teams Must Fix Before November 3
  • AI Agents Shouldn't Hold the Keys to Their Own Audit Log
  • Running a SaaS Audit Without a Dedicated IT Team

Start by sorting findings into categories, not a single list

A flat list of findings, mixed together with no structure, tends to overwhelm whoever's supposed to act on it. Sorting results into a few clear categories makes the next steps obvious rather than something that has to be figured out fresh for each item.

Immediate action items. Findings that are unambiguous and low-risk to act on right away: a license tied to an employee who left the company months ago, a duplicate subscription nobody disputes is redundant. These don't need a debate, they need someone to actually do the thing.

Renewal-timed decisions. Findings that make sense to address at the next contract renewal rather than immediately, like a tool running at 40% utilization where downgrading the plan tier mid-contract isn't practical, but adjusting it at renewal clearly is.

Findings that need further investigation. Anything genuinely unclear, an application with no identifiable owner, a tool whose actual business purpose nobody can confirm. These shouldn't be acted on hastily, but they also shouldn't sit unresolved indefinitely just because the answer isn't obvious yet.

Structural or process findings. Issues that point to a gap in how software gets adopted or reviewed in the first place, rather than a one-off waste item. A pattern of tools entering the stack with no approval process, for instance, is a finding about the process itself, not just the individual tools it produced.

Assign every finding a decision, an owner, and a deadline

A finding without an owner is a finding that won't get resolved, regardless of how clearly it's documented. The specific phrasing matters here: "cancel unused Figma seats" is an observation. "Cancel 8 unused Figma seats, owner: design lead, done by end of month" is something that actually happens, because it names who's responsible and by when.

Assign a person, not a team. The same principle that applies to application ownership applies to audit findings: a finding assigned to "IT" diffuses responsibility across everyone and therefore no one in particular.

Set a realistic deadline, and track it. A finding with no deadline tends to sit indefinitely, competing against everything else that feels more urgent in the moment. A short, defined window keeps it from quietly falling off everyone's radar.

Estimate the financial impact where you can. Even a rough dollar figure attached to a finding, unused-license savings, contract right-sizing, gives the resolution real weight in a way a purely descriptive finding doesn't, and it's what makes the audit's value legible to finance and leadership later.

Report on what actually changed, not just what was found

A list of findings is useful to the team that ran the audit. What actually changed as a result is what matters to everyone else, and the two are easy to conflate if the reporting stops at "here's what we found."

Track realized savings against identified savings. An audit that identifies $80,000 in potential savings is only worth as much as what actually gets executed. Reporting the gap between identified and realized, and why it exists where it does, is what makes a second audit worth funding.

Report resolution rate on structural findings specifically, not just cost items. A process gap identified last quarter that's still unaddressed this quarter is worth flagging on its own, separate from whether individual cost findings got resolved.

Keep a running comparison across audit cycles. Whether the same categories of waste keep reappearing, or whether previous fixes are actually holding, tells you more about whether your underlying process is improving than any single audit's findings do in isolation.

Fix the process, not just the individual findings

The most valuable output of a thorough audit is often not the specific waste it identifies, but what that waste reveals about a gap in the underlying process. Finding twelve licenses tied to former employees is a useful, immediate fix. Recognizing that all twelve trace back to an offboarding process that never included license deactivation is the finding that prevents the same problem from recurring at the next audit.

Ask "why did this happen" for every recurring category of finding. A single unused license is a one-off. A pattern of unused licenses tied to the same root cause, whether that's offboarding, renewal timing, or unclear ownership, points to something worth fixing structurally.

Update the process that let the gap form, not just the symptom. If duplicate tools keep appearing because there's no check before a new purchase gets approved, adding that check prevents the next audit from finding the same category of waste all over again.

What tends to undermine this stage

Treating the audit as complete once the findings are documented. The findings are the input to the actual work, not the deliverable itself. An audit that ends with a report, rather than a set of assigned, tracked actions, produces very little lasting value.

Letting findings pile up without prioritization. Not every finding deserves equal urgency, and treating everything as equally important tends to mean nothing gets done first, since there's no clear signal about where to start.

Never closing the loop on what was decided. Findings marked "needs investigation" that never get revisited become permanent unresolved items, indistinguishable from findings that were simply never addressed at all.

Where OptyStack fits

Tracking which findings were acted on, by whom, and what the actual financial impact turned out to be is difficult to sustain in a spreadsheet that isn't connected to the underlying spend and usage data it's describing.

OptyStack keeps application, spend, and usage data current across your SaaS estate, so tracking whether an identified waste item was actually resolved, and confirming the savings materialized, doesn't require a separate manual reconciliation after the fact.

It's free to start and doesn't require a credit card.

Turn your audit findings into tracked, resolved action. Start free with OptyStack.
Unlock visibility. Slash SaaS waste.

Get real-time SaaS spend insights, discovery, and optimization in OptyStack Hub—start free, no credit card required.

Sign up for OptyStack Hub
PreviousMeasuring SaaS Utilisation: The Metrics That MatterNextSaaS Audit Mistakes That Cost Companies Money

Related articles

  • How to Offboard an Employee's AI Agents: A Checklist for IT Teams
    Best Practices

    How to Offboard an Employee's AI Agents: A Checklist for IT Teams

    Employees leave, but the AI agents they created and connected can keep running with active credentials. This checklist helps IT teams find every agent, OAuth grant, and API key tied to a departing employee, reassign or retire it, revoke access, and reclaim unused licenses.

    Oct 30, 2026

  • Microsoft Entra MemberOf Retirement: What IT Teams Must Fix Before November 3
    Best Practices

    Microsoft Entra MemberOf Retirement: What IT Teams Must Fix Before November 3

    Microsoft Entra is ending the preview of the MemberOf rule operator on November 3, 2026. Learn which configurations are affected, how to find them, and what to replace them with before group membership and access assignments stop updating.

    Oct 26, 2026

  • AI Agents Shouldn't Hold the Keys to Their Own Audit Log
    Best Practices

    AI Agents Shouldn't Hold the Keys to Their Own Audit Log

    AI agents can access systems, use credentials, and take actions that are difficult to audit. Learn five practical controls for agent inventories, least privilege, independent logging, access reviews, and secure offboarding.

    Oct 23, 2026

  • Running a SaaS Audit Without a Dedicated IT Team
    Best Practices

    Running a SaaS Audit Without a Dedicated IT Team

    Running a SaaS audit doesn't require a dedicated IT department. Here's a practical approach for small teams using financial records, available identity data, team input, and a lightweight process that can be maintained over time.

    Sep 25, 2026

  • SaaS Audit Mistakes That Cost Companies Money
    Best Practices

    SaaS Audit Mistakes That Cost Companies Money

    A thorough audit and an effective one aren't the same thing. Here are the SaaS audit mistakes that quietly cost the most, from confusing contract end dates with notice deadlines to letting identified savings never turn into realized ones.

    Sep 24, 2026

Keep reading

More guides on SaaS visibility, spend, and governance—jump between topics without leaving the blog.

View all posts →
  • Conditional Access for AI Agents: What Mid-Market Teams Without Microsoft E7 Should Do
    SaaS Governance

    Conditional Access for AI Agents: What Mid-Market Teams Without Microsoft E7 Should Do

    Microsoft has announced dynamic permissions and agent risk controls, while Entra Conditional Access policy plans are in preview. This guide explains the licensing routes and shows mid-market teams how to inventory applications, OAuth grants and agents, apply least privilege, enforce SSO and review access.

  • Shadow AI Is Not a Tool List: What One in Five Surveyed Organisations Reveals About AI Risk
    SaaS Governance

    Shadow AI Is Not a Tool List: What One in Five Surveyed Organisations Reveals About AI Risk

    A DNSFilter survey found that 20.1% of surveyed organisations said an unapproved AI connection had caused a security incident. This guide explains why Shadow AI discovery needs more than an app list, examines recent third-party security incidents and provides a four-step checklist for mapping applications, access and data exposure.

  • NIST's 10 AI Agent Identity Tenets: A Practical Checklist for Indian IT and Security Teams
    SaaS Governance

    NIST's 10 AI Agent Identity Tenets: A Practical Checklist for Indian IT and Security Teams

    NIST has proposed ten design tenets for AI agent identity, treating agents as distinct, least-privilege, and revocable identities with human oversight and tamper-evident logs. This guide explains each tenet, maps it to a practical control, and gives a five-step starting checklist.

  • Torii Alternatives and Freshservice SaaS Management Compared
    SaaS Optimization

    Torii Alternatives and Freshservice SaaS Management Compared

    Freshworks has agreed to acquire Torii and extend Freshservice into SaaS and AI spend management. This guide compares Torii alternatives side by side and sets out what to ask vendors about roadmap, pricing, AI spend coverage, and India support.

  • What the AU Small Finance Bank Leak Teaches Indian Companies About Third-Party SaaS Risk
    Vendor Management

    What the AU Small Finance Bank Leak Teaches Indian Companies About Third-Party SaaS Risk

    The AU Small Finance Bank data leak investigation highlights the risks of relying on third-party SaaS platforms. Explore the November 2 disclosure, five essential security checks, and a practical 30-day plan to strengthen SaaS visibility, access controls and vendor risk management.

  • Stolen AI Keys Are the New Shadow AI Bill

    Stolen AI Keys Are the New Shadow AI Bill

    Stolen AI API keys can turn hidden security gaps into unexpected bills. Explore the October 2026 AI platform breaches and learn how to inventory AI tools, assign key ownership, monitor spending, and revoke exposed credentials before costs escalate.

Ask the smartest LLMs about OptyStack

ChatGPTGeminiClaudePerplexityGrokCopilot
OptyStack LogoOptyStack Logo

The complete SaaS spend visibility and optimization platform. Connect, analyze, and optimize your entire software stack.

Product

  • Features
  • Integrations
  • Pricing
  • API

SaaS Directory

  • Browse All Apps
  • Slack
  • Microsoft 365
  • Salesforce
  • Zoom
  • Zoho One

Features

  • Cost Optimization
  • Shadow IT Discovery
  • License Management
  • Contract Renewals
  • App Integrations
  • Identity & Zero Trust

Tools & Resources

  • ROI Calculator
  • Knowledge Base
  • SaaS Inflation Index
  • Compare Tools
  • Getting started with OptyStack

Company

  • About
  • Blog
  • Success Stories
  • Events
  • Careers
  • Contact
  • Review us on G2

Stay updated

Get the latest insights on SaaS optimization

© 2026 OptyStack. All Rights Reserved.

LegalPrivacy PolicyTerms of Service