OptyStack LogoOptyStack Logo
Product
Features
Cost OptimizationCut SaaS waste with discovery, usage-backed rightsizing, and renewal leverage—often up to ~30% savings.Shadow IT DiscoveryDiscover unsanctioned SaaS, shadow AI, and unmanaged subscriptions in one place.License ManagementFind unused seats, eliminate zombie accounts, and automate renewals with usage-backed data.Contract Renewal TrackingOne renewal calendar with notice windows, usage context, and negotiation-ready briefs.Seamless App IntegrationsConnect Microsoft 365, Google Workspace, SSO, and 100+ SaaS brands into one live inventory.Identity Management with Zero Trust SecuritySingle sign-on and conditional access by IP, device, and region for your SaaS apps.
ROI Calculator
Resources

Support

  • Support
  • Knowledge Base
  • SaaS Directory
  • Partners

Content

  • SaaS Inflation Index
  • 2026 SaaS Audit Toolkit
  • Blogs
  • Success Stories
  • Events
PricingAboutContact
Start Free Trial
Book Demo
← All postsSaaS Governance

Conditional Access for AI Agents: What Mid-Market Teams Without Microsoft E7 Should Do

Abhishek Sharma · November 6, 2026
Professional infographic illustrating conditional access for AI agents, featuring an AI robot, a secure access shield, and a checklist highlighting access controls, security policies, and activity monitoring for mid-market IT teams without Microsoft E7.
Share
LinkedInX

Microsoft has announced dynamic permissions and agent risk controls, while Entra Conditional Access policy plans are in preview. This guide explains the licensing routes and shows mid-market teams how to inventory applications, OAuth grants and agents, apply least privilege, enforce SSO and review access.

Microsoft is developing new controls to govern what AI agents can access and do inside enterprise environments. On October 19, 2026, Microsoft announced Dynamic Permissions, Dynamic Agent Risk and Dynamic Conditional Access for agents. These capabilities are designed to give agents task-specific permissions and adjust their access as risk changes. On October 29, Microsoft also published documentation for Conditional Access policy plans, a preview feature that helps administrators organise shared conditions and rules, including controls for agent activity.

These developments matter, but organisations should understand the licensing requirements before planning around them. Microsoft 365 E7 includes the relevant Agent 365 and Entra capabilities, but E7 is not the only licensing route. Mid-market teams without E7 can use Microsoft Agent 365 with qualifying Entra or Microsoft 365 licences. Teams without those options still need to govern agents, OAuth grants and application access through the controls available in their environments.

Related reading

Explore related guides and continue your SaaS optimization research:

  • Shadow AI Is Not a Tool List: What One in Five Surveyed Organisations Reveals About AI Risk
  • NIST's 10 AI Agent Identity Tenets: A Practical Checklist for Indian IT and Security Teams
  • SaaS Intake Management in : How to Control Software Requests Before They Become Shadow IT
  • Who Pays for the Tokens? A Simple AI Cost Allocation Model for Growing Companies

What Microsoft Announced

Three capabilities from Microsoft's October 19 announcement are particularly relevant.

Dynamic Permissions: Agents begin with no authority and receive only the permissions required for an approved task. Access can be scoped to the task, time-limited and reduced or removed as the task changes or finishes. Higher-impact actions can require verified human approval.

Dynamic Agent Risk: Microsoft combines signals from identity, data, endpoints, cloud, network, runtime and agent activity to continuously assess an agent's risk. The aim is to identify when an agent's behaviour or access no longer matches its intended task.

Dynamic Conditional Access: This extends Conditional Access for agents so that changing risk can trigger graduated responses. These can include preserving read access while blocking writes, narrowing accessible resources, requiring human approval or isolating the agent.

These were announced capabilities; organisations should check Microsoft's current product documentation and tenant availability before assuming they can deploy them.

Source: Microsoft Security – Agents are your newest insiders

What the Licensing Actually Requires

Microsoft Entra Conditional Access for agents is not exclusive to Microsoft 365 E7. Microsoft's current documentation lists two licensing routes:

  • Microsoft 365 E7, which includes Agent 365 and Microsoft Entra Suite.

  • Microsoft Agent 365 paired with at least Microsoft Entra ID P1 or Microsoft 365 E3.

There is an additional requirement for risk-based agent policies: Microsoft lists Agent 365 paired with Entra ID P2 or Microsoft 365 E5.

This distinction matters. A company without E7 may still qualify for agent-specific Conditional Access through the Agent 365 add-on and the required base licence. Organisations should verify their exact feature entitlements before budgeting or designing policies.

Source: Microsoft Learn – Conditional Access for agents

The Gap: Apps, OAuth Grants and Agents Outside Entra

Conditional Access can only enforce controls along the authentication and resource paths it protects. Microsoft's documentation makes an important boundary clear: Conditional Access protects resources secured by Microsoft Entra ID. If an agent accesses a service directly using an API key, it bypasses Entra's token issuance process, so those Conditional Access policies do not apply.

That leaves teams needing visibility into more than employee sign-ins. Agents may use delegated OAuth permissions, application identities, service accounts or API keys. Some operate through third-party SaaS platforms, while others run as scripts or scheduled automations.

A useful inventory should identify the application or agent, its owner, the identity it uses, the permissions granted, the resources it can reach and the method used to authenticate.

Source: Microsoft Learn – Conditional Access for agents: boundaries and limitations

A Five-Step Checklist for Mid-Market Teams

1. Inventory applications and OAuth grants. Review connected applications in Microsoft 365, Google Workspace and other identity platforms. Include user- and admin-approved OAuth grants. Record the application, owner, permissions, connected users and last-used information where available.

2. Find agents and non-human identities. Look for service accounts, API keys, scheduled automations, MCP connections and AI assistants with access to company systems. Use expense records, identity logs and browser activity as discovery sources. Assign an accountable owner to every identified agent or integration.

3. Apply least privilege. Compare each agent's permissions with its actual task. Remove unnecessary write access, narrow broad integration permissions and separate shared accounts where possible. Use project, resource and time restrictions when the relevant platform supports them.

4. Enforce SSO and sign-in conditions. Route supported applications through SSO. Apply conditions such as approved IP addresses, devices and regions where your identity and application setup supports them. Test policies in report-only or equivalent modes before enforcement, and maintain emergency access procedures.

5. Monitor and review access. Review application inventories and permissions regularly. Investigate new OAuth grants, unexpected sign-ins and access outside an agent's approved scope. Revoke unnecessary access when employees leave, agents are retired or integrations are no longer required.

Where OptyStack Fits

OptyStack helps organisations improve visibility into SaaS and AI applications. Its discovery capabilities use spend, SSO and browser signals to identify applications, map usage to users and surface potential Shadow IT and Shadow AI activity.

For human-user access to connected third-party applications, OptyStack acts as an identity broker. It imports users from Google Workspace, Microsoft or Okta and checks sign-ins against configured IP address, device and region conditions. If a condition is not met, access to the connected app is denied.

These capabilities support application discovery and human-user sign-in control. They should not be confused with Microsoft's agent-specific identity controls. OptyStack does not provide Dynamic Permissions or Dynamic Agent Risk, issue identities to AI agents, or replace dedicated API-key and secrets-management controls.

Learn more about OptyStack identity management.

Start With Visibility

Conditional access for AI agents begins with knowing which applications, identities and integrations exist. Microsoft is building more specialised controls, but licensing, resource coverage and authentication methods determine where those controls can actually apply.

Mid-market teams should start by inventorying applications and agents, identifying how they authenticate, reducing unnecessary permissions and enforcing the sign-in controls available to them. That creates a stronger foundation for adopting agent-specific controls as their licensing and platforms allow.

Create an OptyStack account to explore SaaS and AI application visibility.
Unlock visibility. Slash SaaS waste.

Get real-time SaaS spend insights, discovery, and optimization in OptyStack Hub—start free, no credit card required.

Sign up for OptyStack Hub
PreviousShadow AI Is Not a Tool List: What One in Five Surveyed Organisations Reveals About AI Risk

Related articles

  • Shadow AI Is Not a Tool List: What One in Five Surveyed Organisations Reveals About AI Risk
    SaaS Governance

    Shadow AI Is Not a Tool List: What One in Five Surveyed Organisations Reveals About AI Risk

    A DNSFilter survey found that 20.1% of surveyed organisations said an unapproved AI connection had caused a security incident. This guide explains why Shadow AI discovery needs more than an app list, examines recent third-party security incidents and provides a four-step checklist for mapping applications, access and data exposure.

    Nov 5, 2026

  • NIST's 10 AI Agent Identity Tenets: A Practical Checklist for Indian IT and Security Teams
    SaaS Governance

    NIST's 10 AI Agent Identity Tenets: A Practical Checklist for Indian IT and Security Teams

    NIST has proposed ten design tenets for AI agent identity, treating agents as distinct, least-privilege, and revocable identities with human oversight and tamper-evident logs. This guide explains each tenet, maps it to a practical control, and gives a five-step starting checklist.

    Nov 4, 2026

  • SaaS Intake Management in : How to Control Software Requests Before They Become Shadow IT
    SaaS Governance

    SaaS Intake Management in : How to Control Software Requests Before They Become Shadow IT

    New software requests can introduce security risks, duplicate tools, and unexpected costs. Learn how a structured SaaS intake management process helps IT teams evaluate requests, control software adoption, and improve visibility.

    Oct 28, 2026

  • Who Pays for the Tokens? A Simple AI Cost Allocation Model for Growing Companies
    SaaS Governance

    Who Pays for the Tokens? A Simple AI Cost Allocation Model for Growing Companies

    Seat counts no longer explain AI bills. Learn how to inventory AI tools and agents, assign owners and budgets, track usage against spend, and bring better cost visibility into contract renewals.

    Oct 27, 2026

  • AI Agent Offboarding: A Joiner-Mover-Leaver Checklist for People and Bots
    SaaS Governance

    AI Agent Offboarding: A Joiner-Mover-Leaver Checklist for People and Bots

    Workday’s deal for C1.ai and reported bank-regulator questions about AI agent limits and shutdowns show how seriously agent lifecycle is being treated. Here’s a joiner-mover-leaver checklist for registering, re-scoping and retiring AI agents alongside people.

    Oct 14, 2026

Keep reading

More guides on SaaS visibility, spend, and governance—jump between topics without leaving the blog.

View all posts →
  • Torii Alternatives and Freshservice SaaS Management Compared
    SaaS Optimization

    Torii Alternatives and Freshservice SaaS Management Compared

    Freshworks has agreed to acquire Torii and extend Freshservice into SaaS and AI spend management. This guide compares Torii alternatives side by side and sets out what to ask vendors about roadmap, pricing, AI spend coverage, and India support.

  • What the AU Small Finance Bank Leak Teaches Indian Companies About Third-Party SaaS Risk
    Vendor Management

    What the AU Small Finance Bank Leak Teaches Indian Companies About Third-Party SaaS Risk

    The AU Small Finance Bank data leak investigation highlights the risks of relying on third-party SaaS platforms. Explore the November 2 disclosure, five essential security checks, and a practical 30-day plan to strengthen SaaS visibility, access controls and vendor risk management.

  • Stolen AI Keys Are the New Shadow AI Bill

    Stolen AI Keys Are the New Shadow AI Bill

    Stolen AI API keys can turn hidden security gaps into unexpected bills. Explore the October 2026 AI platform breaches and learn how to inventory AI tools, assign key ownership, monitor spending, and revoke exposed credentials before costs escalate.

  • How to Offboard an Employee's AI Agents: A Checklist for IT Teams
    Best Practices

    How to Offboard an Employee's AI Agents: A Checklist for IT Teams

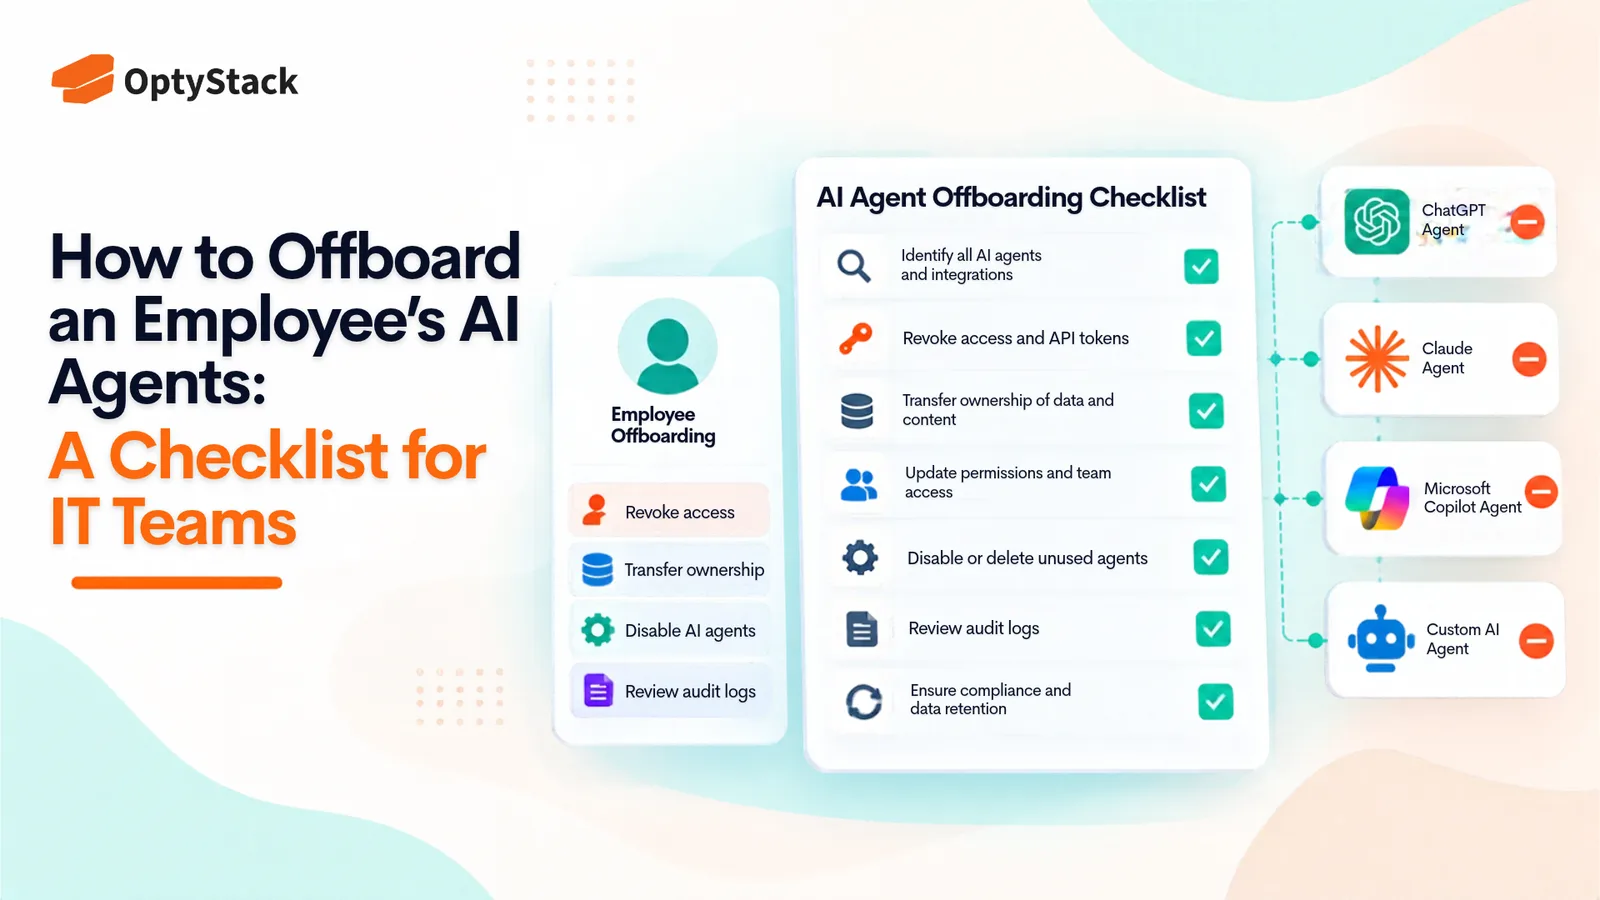
    Employees leave, but the AI agents they created and connected can keep running with active credentials. This checklist helps IT teams find every agent, OAuth grant, and API key tied to a departing employee, reassign or retire it, revoke access, and reclaim unused licenses.

  • AI Security Checklist for Businesses: How to Assess AI Features in SaaS Tools
    Vendor Management

    AI Security Checklist for Businesses: How to Assess AI Features in SaaS Tools

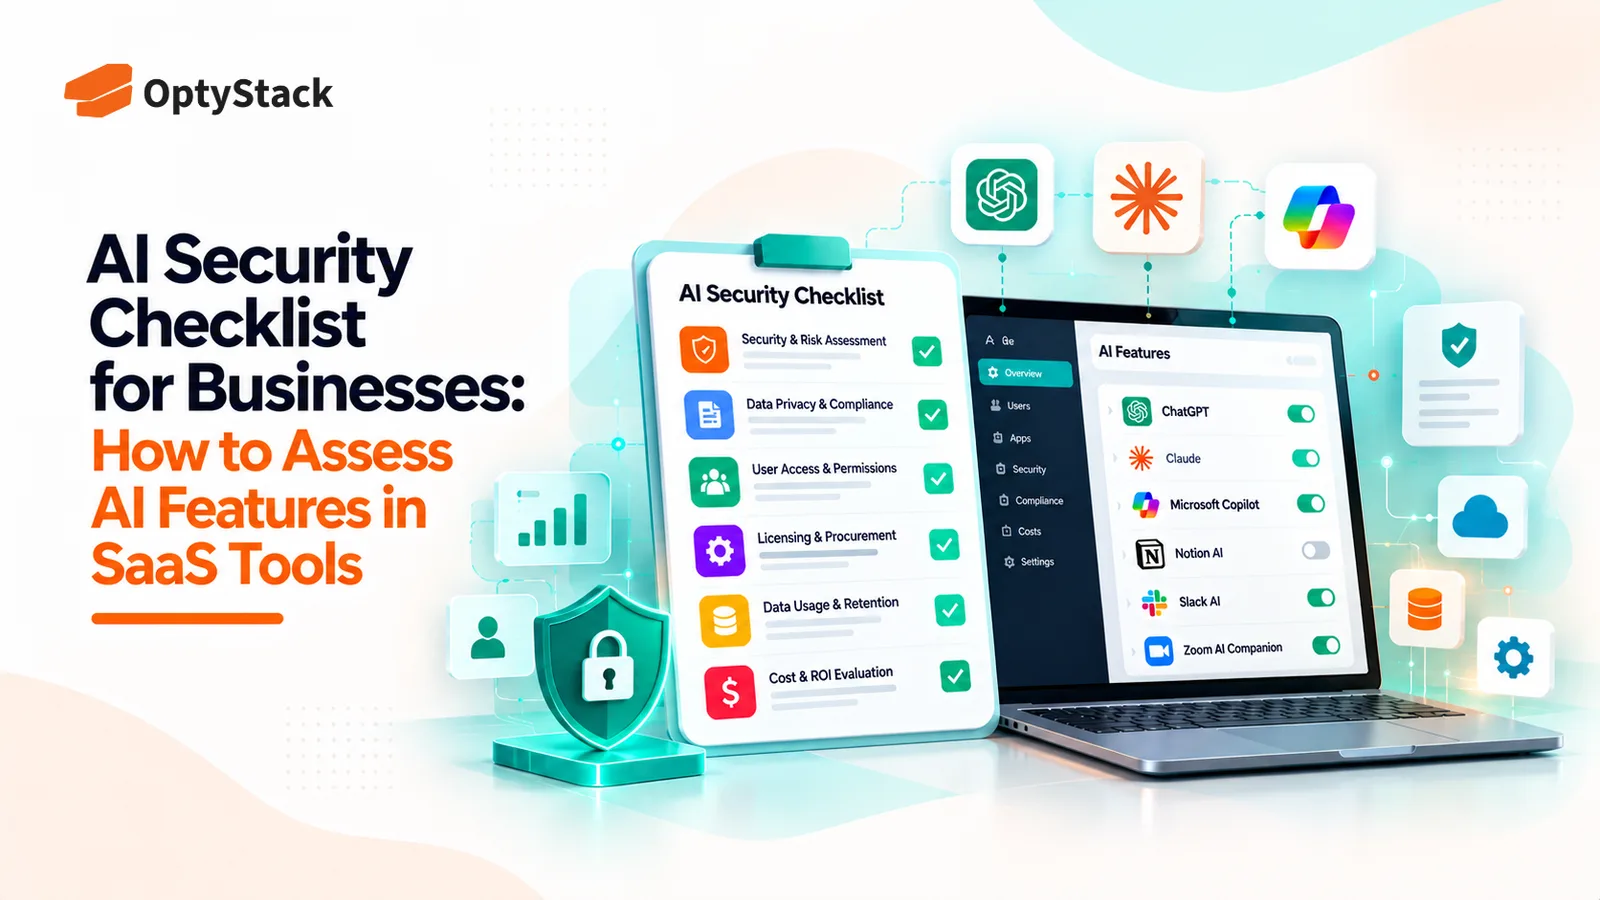
    AI features are appearing inside the SaaS tools businesses already use. Before enabling them, review what data they can access, how vendors process information, which controls are available, and whether the feature introduces new costs or risks.

  • How to Track AI Spend Per User Across GitHub Copilot, Claude, and ChatGPT
    Cost Management

    How to Track AI Spend Per User Across GitHub Copilot, Claude, and ChatGPT

    Seat counts no longer explain every AI bill. GitHub Copilot, Claude, and ChatGPT offer different usage reports and spending controls. Learn how to combine vendor billing data, identity logs, and expense records into one per-user view.

Ask the smartest LLMs about OptyStack

ChatGPTGeminiClaudePerplexityGrokCopilot
OptyStack LogoOptyStack Logo

The complete SaaS spend visibility and optimization platform. Connect, analyze, and optimize your entire software stack.

Product

  • Features
  • Integrations
  • Pricing
  • API

SaaS Directory

  • Browse All Apps
  • Slack
  • Microsoft 365
  • Salesforce
  • Zoom
  • Zoho One

Features

  • Cost Optimization
  • Shadow IT Discovery
  • License Management
  • Contract Renewals
  • App Integrations
  • Identity & Zero Trust

Tools & Resources

  • ROI Calculator
  • Knowledge Base
  • SaaS Inflation Index
  • Compare Tools
  • Getting started with OptyStack

Company

  • About
  • Blog
  • Success Stories
  • Events
  • Careers
  • Contact
  • Review us on G2

Stay updated

Get the latest insights on SaaS optimization

© 2026 OptyStack. All Rights Reserved.

LegalPrivacy PolicyTerms of Service