OptyStack Blog
Insights, tips, and strategies for optimizing your SaaS stack and maximizing your software investments.
AI Agent Offboarding: A Joiner-Mover-Leaver Checklist for People and Bots
Workday’s deal for C1.ai and reported bank-regulator questions about AI agent limits and shutdowns show how seriously agent lifecycle is being treated. Here’s a joiner-mover-leaver checklist for registering, re-scoping and retiring AI agents alongside people.
Aryan Malik
Shadow Agents Are the New Shadow IT: What SaaS Management Must Cover in 2026
AI agents can access tools, use credentials, and move data through existing SaaS applications. Learn why traditional SaaS inventories may miss agent-level activity and how to build a practical discovery and governance process.
Aryan Malik
SaaS Management vs IT Asset Management Tools
ITAM and SaaS management overlap, but they are designed around different priorities. Learn how the two approaches differ, where they complement each other, and how to decide which tools your organization actually needs.
Aryan Malik
AI Tool Governance for Mid-Market Companies
Mid-market companies are the least mature of any size band on AI governance, despite having real risk and real scale. Here's why enterprise governance frameworks are hard to run at this size, and what a lean, workable approach actually looks like instead.
Aryan Malik
How to Write an AI Acceptable-Use Policy
Employees are already using AI tools, whether or not an organization has finished writing its policy. Learn what an AI acceptable-use policy should cover, how to build one step by step, and how to keep it aligned with real-world AI usage.
Aryan Malik
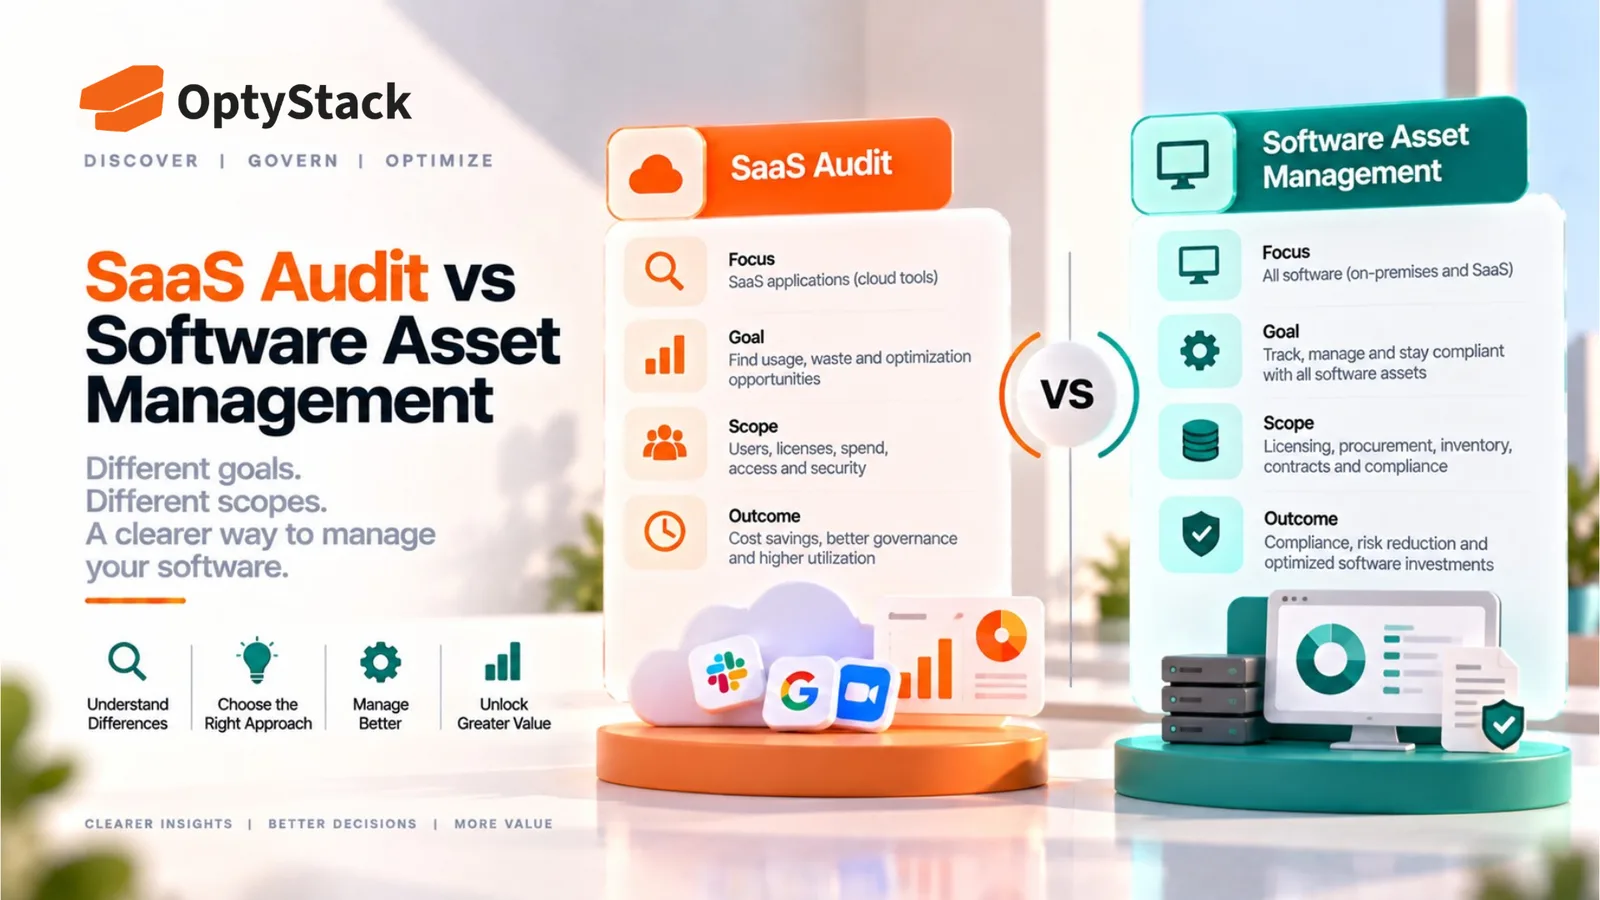
SaaS Audit vs Software Asset Management
A SaaS audit is a periodic review. Software asset management is an ongoing discipline. Learn how the two differ, how they work together, and how companies can move from one-time audits toward continuous software management.
Aryan Malik
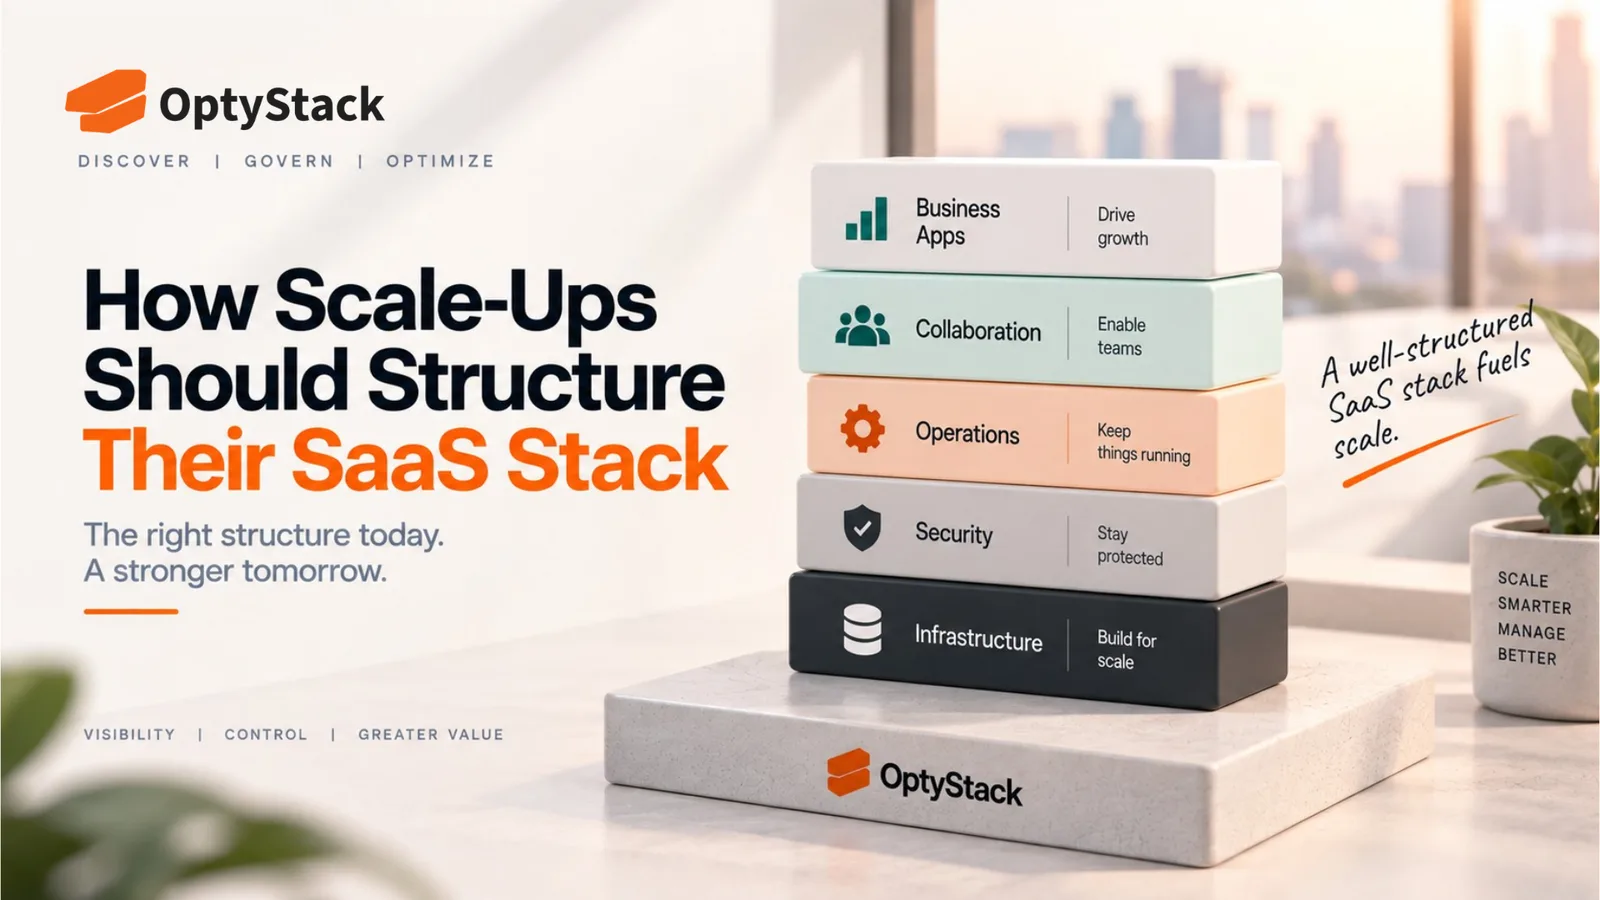
How Scale-Ups Should Structure Their SaaS Stack
The gap between startup and enterprise is where SaaS sprawl usually takes root, as headcount and tool adoption both outpace any process built to manage them. Here's how scale-ups should structure their SaaS stack at each stage of growth.
Aryan Malik
SaaS Governance: How to Get Executive Buy-In
Most governance initiatives stall because nothing makes the risk feel urgent to leadership. Here's how to build a SaaS governance proposal around real numbers from your own environment, framed in terms executives already prioritize.
Aryan Malik
Least Privilege in SaaS: How to Control User Access
In 2024, stolen credentials gave attackers access to roughly 165 Snowflake customer environments, underscoring how access left unmanaged becomes a long-term risk. Here's how least privilege actually works in a SaaS environment, why it drifts so easily, and how to build a process that keeps it under control.
Aryan Malik