OptyStack Blog
Insights, tips, and strategies for optimizing your SaaS stack and maximizing your software investments.
SaaS Vendor Management Best Practices
Uptime Institute found that 10% of major outages originate with a vendor, and over half cost more than $100,000. Here's how to manage SaaS vendor relationships across the full lifecycle, not just at the point of purchase.
Aryan Malik
SaaS Vendor Breach Response: What to Do When a Vendor Is Breached
When Drift was breached in 2025, over 700 downstream organizations were exposed through a connection they trusted. Here's what to actually do in the first 48 hours after learning a vendor was breached, and how to assess your real exposure fast.
Aryan Malik
SaaS Security Review: How to Build a Process That Works
Most SaaS security reviews happen too late, evaluate a self-reported questionnaire instead of real evidence, and aim for a pass or fail when risk isn't actually binary. Here's how to build a review process that catches real risk, including the tools that never go through one at all.
Aryan Malik
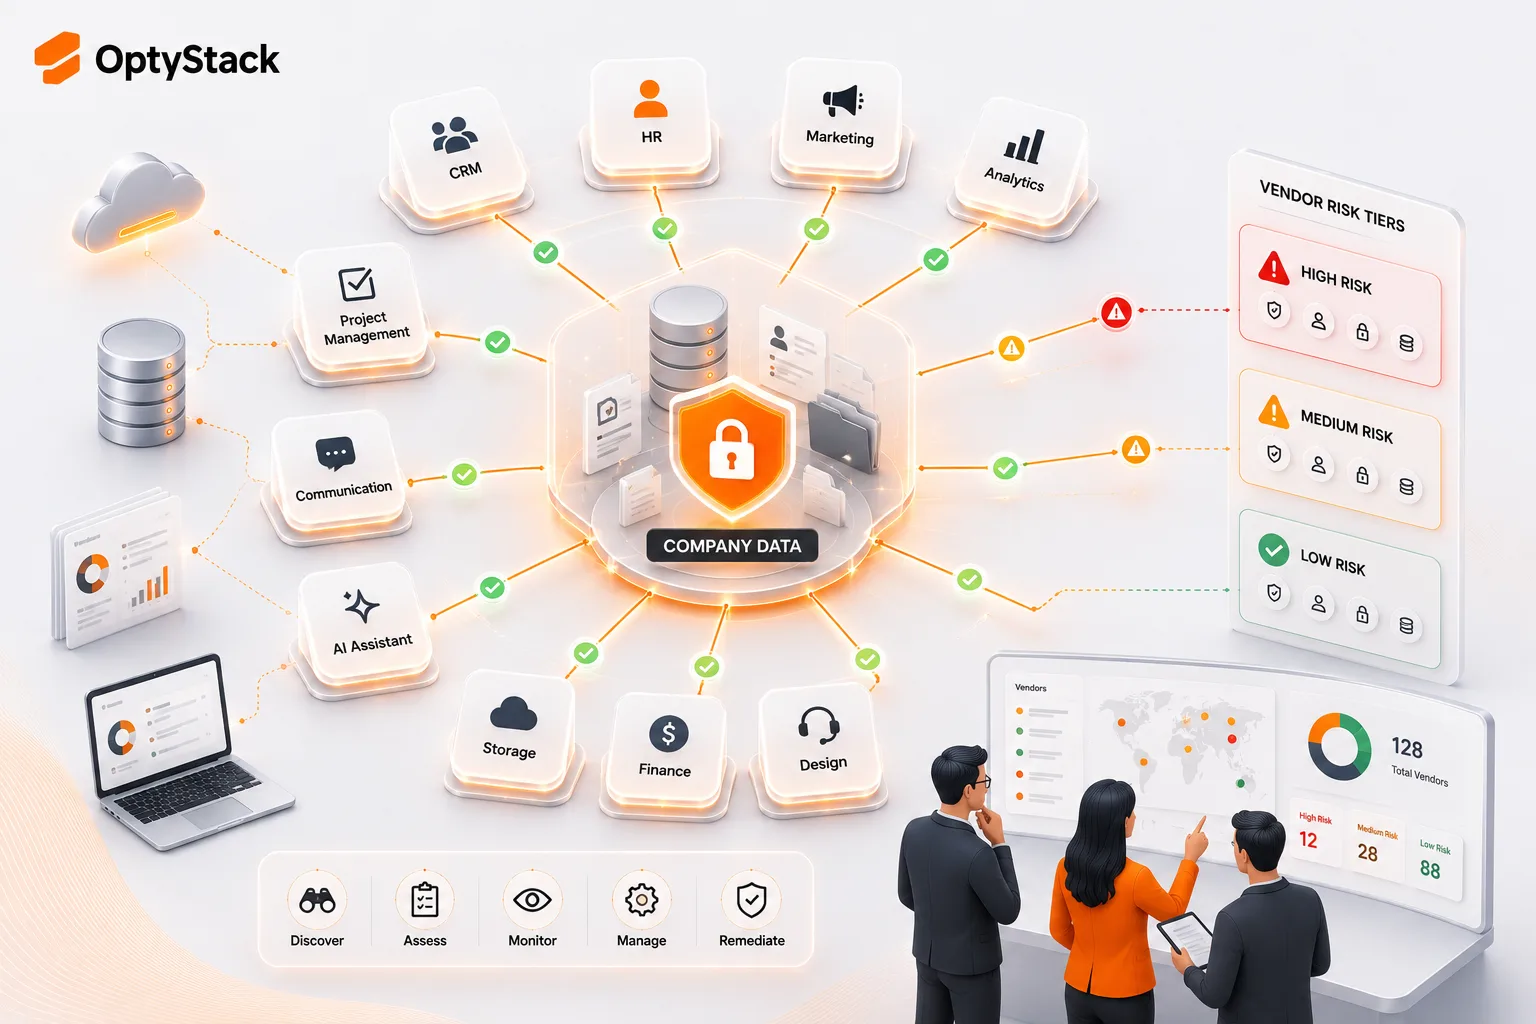
Third-Party Risk Management (TPRM) for SaaS Vendors: A 2026 Guide
Every SaaS vendor you use is a door into your data — and a majority of breaches now involve a third party. This is the 2026 guide to third-party risk management for SaaS: the lifecycle, how to tier vendors by risk, and why annual SOC 2 collection isn't enough.
Hemant Wadhwani
Redefining ROI: A CIO’s Guide to Holistic SaaS Procurement
In a SaaS-driven enterprise, procurement is no longer a discrete purchasing event; it is a continuous, strategic IT lever. CIOs must shift from simply approving the vendor invoice to leading a holistic procurement framework that calculates actual Total Cost of Ownership by weighing subscription fees against security liabilities and operational friction.
Amit Dangi