OptyStack LogoOptyStack Logo
Product
Features
Cost OptimizationCut SaaS waste with discovery, usage-backed rightsizing, and renewal leverage—often up to ~30% savings.Shadow IT DiscoveryDiscover unsanctioned SaaS, shadow AI, and unmanaged subscriptions in one place.License ManagementFind unused seats, eliminate zombie accounts, and automate renewals with usage-backed data.Contract Renewal TrackingOne renewal calendar with notice windows, usage context, and negotiation-ready briefs.Seamless App IntegrationsConnect Microsoft 365, Google Workspace, SSO, and 100+ SaaS brands into one live inventory.Identity Management with Zero Trust SecuritySingle sign-on and conditional access by IP, device, and region for your SaaS apps.
ROI Calculator
Resources

Support

  • Support
  • Knowledge Base
  • SaaS Directory
  • Partners

Content

  • SaaS Inflation Index
  • 2026 SaaS Audit Toolkit
  • Blogs
  • Success Stories
  • Events
PricingAboutContact
Start Free Trial
Book Demo
← All postsShadow IT

Browser Extensions in the Enterprise: Security Risk and Inventory Tactics

Anand Kumar · April 6, 2026
Browser Extensions in the Enterprise: Security Risk and Inventory Tactics
Share
LinkedInX

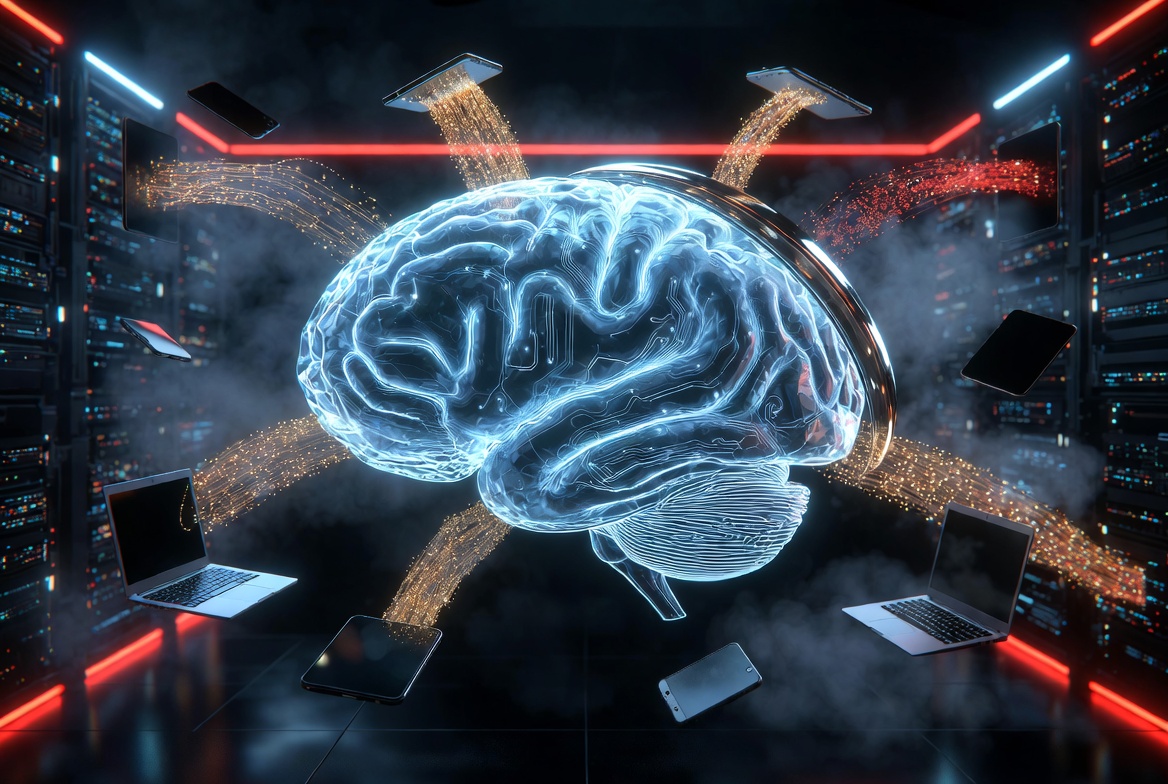
Extensions can exfiltrate page content and credentials. Learn how security teams inventory browser add-ons, separate benign productivity helpers from high-risk data access, and partner with IT without blocking every install.

Modern work happens in the browser. Extensions that summarize pages, check grammar, or inject AI assistance are one click away—and many request broad permissions that mirror the sensitivity of the sites employees visit. Security teams cannot treat extensions as trivia; they are executable code with access to SSO sessions, customer support portals, and internal admin consoles.

Classify by permission, not by brand

A well-known brand name does not guarantee least privilege. Review manifests for permissions like “read and change all your data on all websites” or broad clipboard access. High-risk extensions warrant allowlisting only after security review; medium-risk may be available in a managed catalog; low-risk productivity aids can be self-service with telemetry.

Related reading

Explore related guides and continue your SaaS optimization research:

  • Shadow AI Is a SaaS Visibility Problem: How to Build One Inventory for Apps, AI Tools and Agents
  • OptyStack vs JumpCloud SaaS Management: Discovery, Identity, and Fit for Mid-Market Teams
  • ServiceNow AI Control Tower Alternative: How to Find Shadow AI Today
  • Shadow AI Discovery Beyond the Identity Provider: What Your SSO Can’t See

Where enterprise browsers support extension policies, enforce separation: development environments may allow broader experimentation; customer-facing roles get stricter defaults.

Operational discovery

Endpoint management and browser management tools can report installed extensions, but coverage varies by OS and BYOD policy. Combine those signals with network and CASB visibility where available. The goal is not perfection on day one—it is trending down unknowns quarter over quarter.

Partnering with employees

Blanket bans drive shadow behavior. Publish a short request path for new extensions, with SLAs that respect business deadlines. When you remove a risky add-on, point users to an approved alternative. Communication turns enforcement into partnership.

OptyStack complements technical controls by highlighting unsanctioned SaaS and AI surfaces—including long-tail browser tools—so security and IT leaders prioritize what matters most.

Metrics and maturity

Track coverage percentage: devices or browsers where you have extension visibility, and trend unknowns downward. Pair with incident retrospectives—when data leaves through an extension, trace whether policy, tooling, or training failed. Mature programs review the allowlist quarterly and retire vendors that no longer justify their permission footprint.
Unlock visibility. Slash SaaS waste.

Get real-time SaaS spend insights, discovery, and optimization in OptyStack Hub—start free, no credit card required.

Sign up for OptyStack Hub
PreviousBuilding a Translation Layer Between Finance and IT for SaaS SpendNextUsing Accounts Payable Signals to Supercharge SaaS Discovery

Related articles

  • Shadow AI Is a SaaS Visibility Problem: How to Build One Inventory for Apps, AI Tools and Agents
    Shadow IT

    Shadow AI Is a SaaS Visibility Problem: How to Build One Inventory for Apps, AI Tools and Agents

    Shadow AI extends beyond chatbots into browser extensions, laptop agents, MCP servers, and OAuth-connected applications. Learn how to build one inventory for ownership, data access, cost, and lifecycle management.

    Oct 22, 2026

  • OptyStack vs JumpCloud SaaS Management: Discovery, Identity, and Fit for Mid-Market Teams
    Shadow IT

    OptyStack vs JumpCloud SaaS Management: Discovery, Identity, and Fit for Mid-Market Teams

    JumpCloud and OptyStack both find unsanctioned SaaS, but they start from different places. This comparison covers how each discovers apps, how each handles identity, what OptyStack costs in INR, and which team each one suits.

    Oct 22, 2026

  • ServiceNow AI Control Tower Alternative: How to Find Shadow AI Today
    Shadow IT

    ServiceNow AI Control Tower Alternative: How to Find Shadow AI Today

    ServiceNow is expanding its AI governance platform with shadow AI detection and AI Cost Management. Learn how to compare its announced capabilities with SaaS management alternatives for application discovery, spend visibility and license optimization.

    Oct 19, 2026

  • Shadow AI Discovery Beyond the Identity Provider: What Your SSO Can’t See
    Shadow IT

    Shadow AI Discovery Beyond the Identity Provider: What Your SSO Can’t See

    Nearly half of enterprise AI conversations run through personal accounts, according to Akamai’s 2026 telemetry. Here’s why SSO logs miss them and how to find shadow AI through spend, browser and OAuth signals.

    Oct 12, 2026

  • Browser Extensions: The Overlooked Security Risk
    Shadow IT

    Browser Extensions: The Overlooked Security Risk

    A poisoned VS Code extension compromised a GitHub employee device in 2026, with GitHub saying an attacker's claim of roughly 3,800 exfiltrated internal repositories was directionally consistent with its investigation. Here's why extension security deserves more attention.

    Oct 1, 2026

Keep reading

More guides on SaaS visibility, spend, and governance—jump between topics without leaving the blog.

View all posts →
  • AI Credits at Renewal: A Finance Checklist for Usage-Priced SaaS
    SaaS Renewals Management

    AI Credits at Renewal: A Finance Checklist for Usage-Priced SaaS

    AI credits and usage-based pricing make SaaS renewals harder to forecast. Learn how Finance and Procurement can review allowances, control overages, and prepare 90 days before renewal.

  • How to Plan Your 2027 SaaS Budget: A Practical Guide for Finance and IT Teams

    How to Plan Your 2027 SaaS Budget: A Practical Guide for Finance and IT Teams

    Build a reliable 2027 SaaS budget by consolidating software spending, reviewing renewals, identifying unused licenses, and forecasting AI and subscription costs. Use this practical guide to align Finance and IT before committing to new software expenses.

  • Per-Employee AI Budgets: Control ChatGPT, Claude and Cursor Costs Without Blocking Adoption
    Cost Management

    Per-Employee AI Budgets: Control ChatGPT, Claude and Cursor Costs Without Blocking Adoption

    AI bills can be difficult to forecast, but blanket bans can slow productive teams down. Learn how to build per-employee AI budgets with baseline allocations, shared usage pools, spending alerts and provider-level controls.

  • Your Backup App Was the Breach: A 30-Minute OAuth App Audit for Microsoft 365

    Your Backup App Was the Breach: A 30-Minute OAuth App Audit for Microsoft 365

    The ConnectWise Cloud Backup incident shows why disabling one application may not be enough. Use this 30-minute Microsoft 365 OAuth app audit to review service-principal sign-ins, search for suspicious credentials, flag excessive permissions and identify dormant apps.

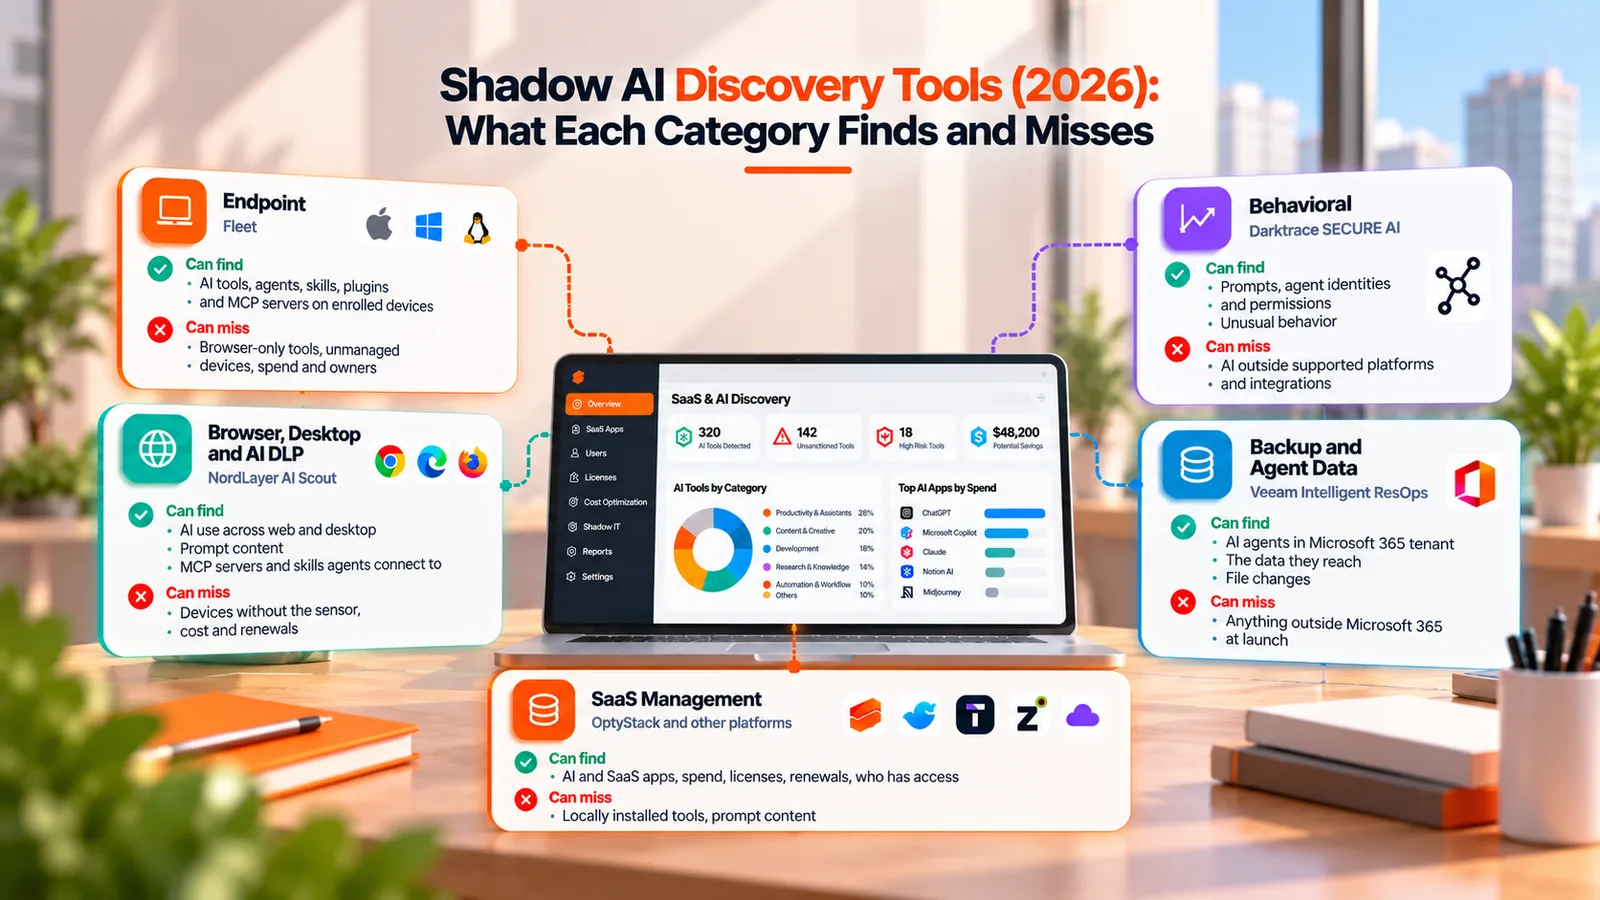
  • Shadow AI Discovery Tools (2026): What Each Category Finds and Misses
    Industry Insights

    Shadow AI Discovery Tools (2026): What Each Category Finds and Misses

    Shadow AI discovery tools aren’t interchangeable. Endpoint, browser and DLP, behavioral, data and SaaS management tools each see a different slice. Here’s what each category finds and misses, with recent launches from Fleet, NordLayer, Darktrace, Veeam and others.

  • Shadow AI Isn't One Tool Category (And That's the Point)
    Industry Insights

    Shadow AI Isn't One Tool Category (And That's the Point)

    NordLayer and Fleet announced new AI visibility capabilities on October 15, 2026, while Veeam launched an adjacent data resilience offering. Darktrace's SECURE AI became generally available in September. Here's how these products differ and what to ask before choosing a tool.

Ask the smartest LLMs about OptyStack

ChatGPTGeminiClaudePerplexityGrokCopilot
OptyStack LogoOptyStack Logo

The complete SaaS spend visibility and optimization platform. Connect, analyze, and optimize your entire software stack.

Product

  • Features
  • Integrations
  • Pricing
  • API

SaaS Directory

  • Browse All Apps
  • Slack
  • Microsoft 365
  • Salesforce
  • Zoom
  • Zoho One

Features

  • Cost Optimization
  • Shadow IT Discovery
  • License Management
  • Contract Renewals
  • App Integrations
  • Identity & Zero Trust

Tools & Resources

  • ROI Calculator
  • Knowledge Base
  • SaaS Inflation Index
  • Compare Tools
  • Getting started with OptyStack

Company

  • About
  • Blog
  • Success Stories
  • Events
  • Careers
  • Contact
  • Review us on G2

Stay updated

Get the latest insights on SaaS optimization

© 2025 OptyStack. All Rights Reserved.

LegalPrivacy PolicyTerms of Service