OptyStack LogoOptyStack Logo
Product
Features
Cost OptimizationCut SaaS waste with discovery, usage-backed rightsizing, and renewal leverage—often up to ~30% savings.Shadow IT DiscoveryDiscover unsanctioned SaaS, shadow AI, and unmanaged subscriptions in one place.License ManagementFind unused seats, eliminate zombie accounts, and automate renewals with usage-backed data.Contract Renewal TrackingOne renewal calendar with notice windows, usage context, and negotiation-ready briefs.Seamless App IntegrationsConnect Microsoft 365, Google Workspace, SSO, and 100+ SaaS brands into one live inventory.Identity Management with Zero Trust SecuritySingle sign-on and conditional access by IP, device, and region for your SaaS apps.
ROI Calculator
Resources

Support

  • Support
  • Knowledge Base
  • SaaS Directory
  • Partners

Content

  • SaaS Inflation Index
  • 2026 SaaS Audit Toolkit
  • Blogs
  • Success Stories
  • Events
PricingAboutContact
Start Free Trial
Book Demo
← All postsShadow IT

Reducing Risk When You Cannot Block Every Unsanctioned App

Ram Kumar · March 28, 2026
Reducing Risk When You Cannot Block Every Unsanctioned App
Share
LinkedInX

Blocking is not always possible. Learn compensating controls: data loss prevention, access reviews, encryption requirements, and phased migration off high-risk shadow tools.

Security teams often want to block unsanctioned applications immediately. Business reality—customer deadlines, inherited stacks, or regional autonomy—means you need a spectrum of responses beyond binary allow/deny.

Prioritize by materiality

Focus on applications that process regulated data, have broad OAuth access, or integrate with source code and customer records. Lower-priority shadow tools can go into a watchlist with periodic review rather than emergency escalation.

Related reading

Explore related guides and continue your SaaS optimization research:

  • Shadow AI Is a SaaS Visibility Problem: How to Build One Inventory for Apps, AI Tools and Agents
  • OptyStack vs JumpCloud SaaS Management: Discovery, Identity, and Fit for Mid-Market Teams
  • ServiceNow AI Control Tower Alternative: How to Find Shadow AI Today
  • Shadow AI Discovery Beyond the Identity Provider: What Your SSO Can’t See

Compensating controls

Where you cannot remove an app overnight, enforce MFA via IdP where possible, tighten DLP rules for uploads to unknown domains, and require annual access certifications for connected identities. Document exceptions with expiry dates so “temporary” does not become permanent.

Migration and consolidation

Offer a sanctioned alternative with migration assistance. Measure duplicate functionality—two project tools or three chat apps—and drive consolidation with clear savings narratives for finance.

Continuous discovery ensures you revisit controls as usage changes; OptyStack helps track which shadow applications remain open risks versus resolved.
Unlock visibility. Slash SaaS waste.

Get real-time SaaS spend insights, discovery, and optimization in OptyStack Hub—start free, no credit card required.

Sign up for OptyStack Hub
PreviousFrom Shadow IT Inventory to Governance: A Practical FrameworkNextProcurement, Finance, and IT: Who Owns Shadow IT Discovery?

Related articles

  • Shadow AI Is a SaaS Visibility Problem: How to Build One Inventory for Apps, AI Tools and Agents
    Shadow IT

    Shadow AI Is a SaaS Visibility Problem: How to Build One Inventory for Apps, AI Tools and Agents

    Shadow AI extends beyond chatbots into browser extensions, laptop agents, MCP servers, and OAuth-connected applications. Learn how to build one inventory for ownership, data access, cost, and lifecycle management.

    Oct 22, 2026

  • OptyStack vs JumpCloud SaaS Management: Discovery, Identity, and Fit for Mid-Market Teams
    Shadow IT

    OptyStack vs JumpCloud SaaS Management: Discovery, Identity, and Fit for Mid-Market Teams

    JumpCloud and OptyStack both find unsanctioned SaaS, but they start from different places. This comparison covers how each discovers apps, how each handles identity, what OptyStack costs in INR, and which team each one suits.

    Oct 22, 2026

  • ServiceNow AI Control Tower Alternative: How to Find Shadow AI Today
    Shadow IT

    ServiceNow AI Control Tower Alternative: How to Find Shadow AI Today

    ServiceNow is expanding its AI governance platform with shadow AI detection and AI Cost Management. Learn how to compare its announced capabilities with SaaS management alternatives for application discovery, spend visibility and license optimization.

    Oct 19, 2026

  • Shadow AI Discovery Beyond the Identity Provider: What Your SSO Can’t See
    Shadow IT

    Shadow AI Discovery Beyond the Identity Provider: What Your SSO Can’t See

    Nearly half of enterprise AI conversations run through personal accounts, according to Akamai’s 2026 telemetry. Here’s why SSO logs miss them and how to find shadow AI through spend, browser and OAuth signals.

    Oct 12, 2026

  • Browser Extensions: The Overlooked Security Risk
    Shadow IT

    Browser Extensions: The Overlooked Security Risk

    A poisoned VS Code extension compromised a GitHub employee device in 2026, with GitHub saying an attacker's claim of roughly 3,800 exfiltrated internal repositories was directionally consistent with its investigation. Here's why extension security deserves more attention.

    Oct 1, 2026

Keep reading

More guides on SaaS visibility, spend, and governance—jump between topics without leaving the blog.

View all posts →
  • Agent Traces Are a Credential Store: What the Cursor Breach Teaches About Identity Risk
    SaaS Governance

    Agent Traces Are a Credential Store: What the Cursor Breach Teaches About Identity Risk

    Cursor’s November 2026 incident update shows how a key issued to a vendor led to exposed agent traces, then to access in SaaS tools, then to a malicious extension. The credentials never passed through a human sign-in. This guide walks through the chain and gives a five-point non-human identity checklist.

  • Cross-Tenant Sync Offboarding: What Microsoft’s Known Issues Mean for Your Checklist
    SaaS Governance

    Cross-Tenant Sync Offboarding: What Microsoft’s Known Issues Mean for Your Checklist

    Cross-tenant sync removes only the users it provisions, and deletion behavior depends on a setting many admins miss. This guide explains Microsoft’s documented limits, adds a Microsoft 365 offboarding checklist, and covers the February 2027 SMS and voice MFA retirement to plan for now.

  • Your AI Vendor’s AI Vendor: What the Fireworks-Notion Breach Teaches About Shadow AI Sub-processors
    SaaS Governance

    Your AI Vendor’s AI Vendor: What the Fireworks-Notion Breach Teaches About Shadow AI Sub-processors

    A breach at AI infrastructure provider Fireworks exposed some Notion AI chat transcripts, and Notion turned off its Insights feature. Notion says its zero data retention promise did not cover that feature. This guide explains the lesson for AI vendor risk and gives a five-step sub-processor inventory.

  • BluePhishing: Why AI Agent Consent Is the New OAuth Blind Spot (and 7 Checks for Your Entra Tenant)
    SaaS Governance

    BluePhishing: Why AI Agent Consent Is the New OAuth Blind Spot (and 7 Checks for Your Entra Tenant)

    Proofpoint’s BluePhishing research shows that one consent to a malicious AI agent blueprint can create up to 250 agent identities in a Microsoft Entra tenant. Those identities skip the controls built for people. This guide explains the proof of concept and gives seven checks for your tenant.

  • Your Vendor’s App Is an Identity Too: 5 Lessons from the MSP Process Breach
    SaaS Governance

    Your Vendor’s App Is an Identity Too: 5 Lessons from the MSP Process Breach

    Stolen app secrets from MSP Process reportedly reached customer Microsoft 365 tenants with no user sign-in and no MFA prompt. This guide explains why MFA and SSO did not help, and gives a five-step third-party app permissions audit covering scopes, owners, secrets, and alerts.

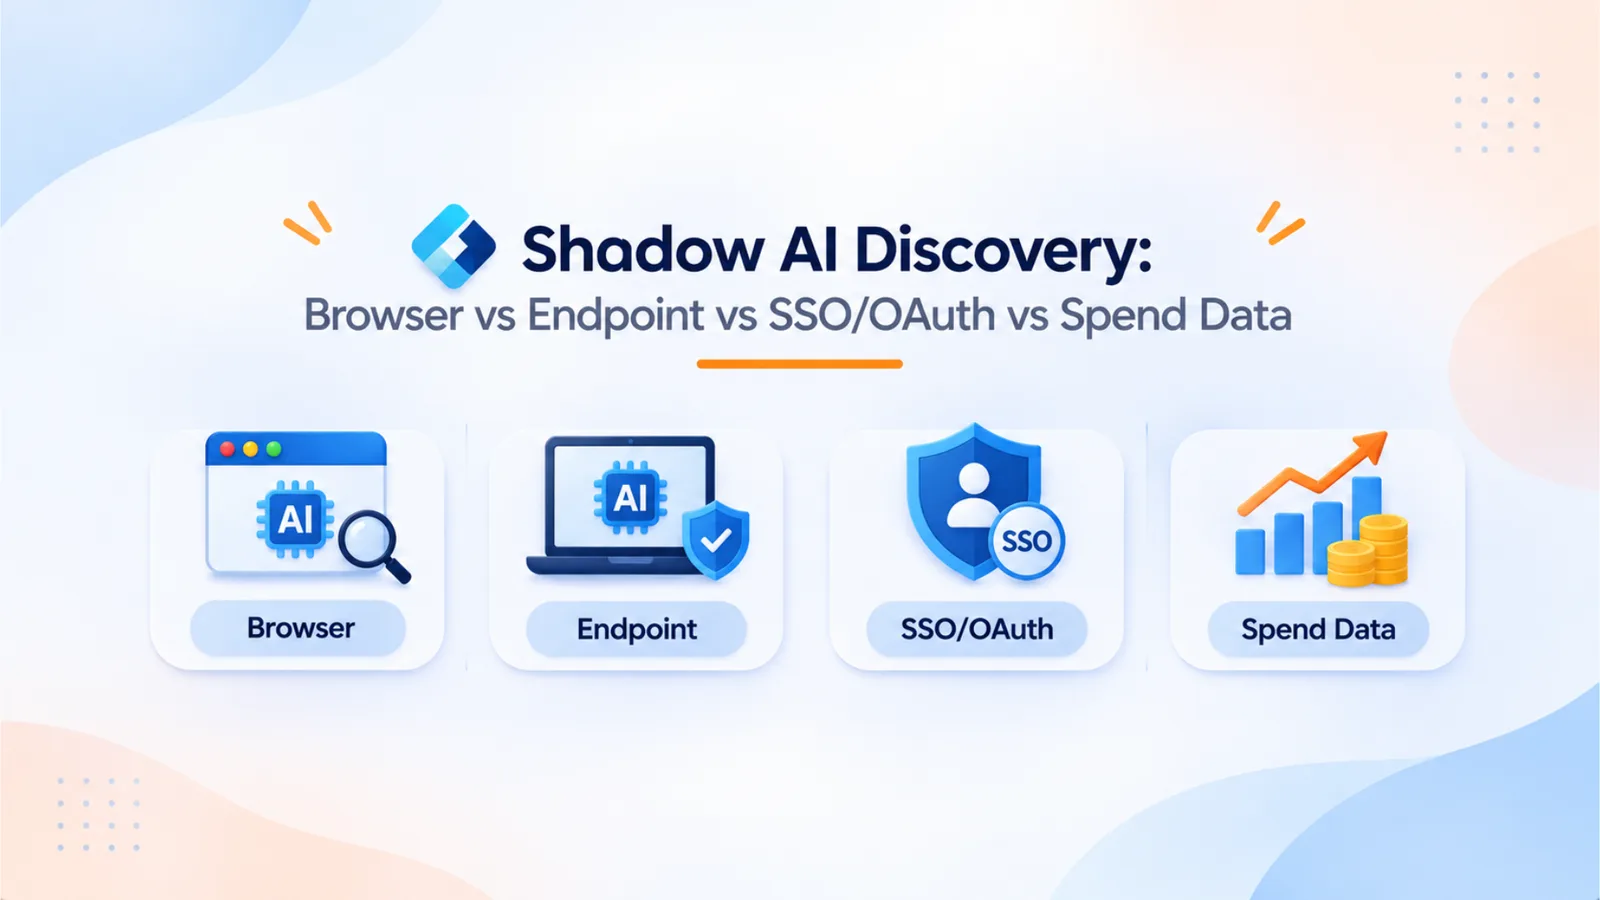
  • Shadow AI Discovery: Browser vs Endpoint vs SSO/OAuth vs Spend Data
    SaaS Governance

    Shadow AI Discovery: Browser vs Endpoint vs SSO/OAuth vs Spend Data

    Shadow AI discovery tools start from different places: the browser, the endpoint, SSO and OAuth grants, or spend data. Each one catches something and misses something. This guide compares the four methods and shows how OptyStack combines SSO, OAuth, browser, and finance signals.

Ask the smartest LLMs about OptyStack

ChatGPTGeminiClaudePerplexityGrokCopilot
OptyStack LogoOptyStack Logo

The complete SaaS spend visibility and optimization platform. Connect, analyze, and optimize your entire software stack.

Product

  • Features
  • Integrations
  • Pricing
  • API

SaaS Directory

  • Browse All Apps
  • Slack
  • Microsoft 365
  • Salesforce
  • Zoom
  • Zoho One

Features

  • Cost Optimization
  • Shadow IT Discovery
  • License Management
  • Contract Renewals
  • App Integrations
  • Identity & Zero Trust

Tools & Resources

  • ROI Calculator
  • Knowledge Base
  • SaaS Inflation Index
  • Compare Tools
  • Getting started with OptyStack

Company

  • About
  • Blog
  • Success Stories
  • Events
  • Careers
  • Contact
  • Review us on G2

Stay updated

Get the latest insights on SaaS optimization

© 2026 OptyStack. All Rights Reserved.

LegalPrivacy PolicyTerms of Service